
Bleeping Computer
What it covers
Latest stories it covered
PHP2Shell RCE flaws exploited against Palo Alto Networks management interfaces and other targets
Multiple security outlets report that attackers are exploiting PHP2Shell—two newly patched critical PHP remote code execution (RCE) flaws, CVE-2026-109618 and CVE-2026-109619—to co...
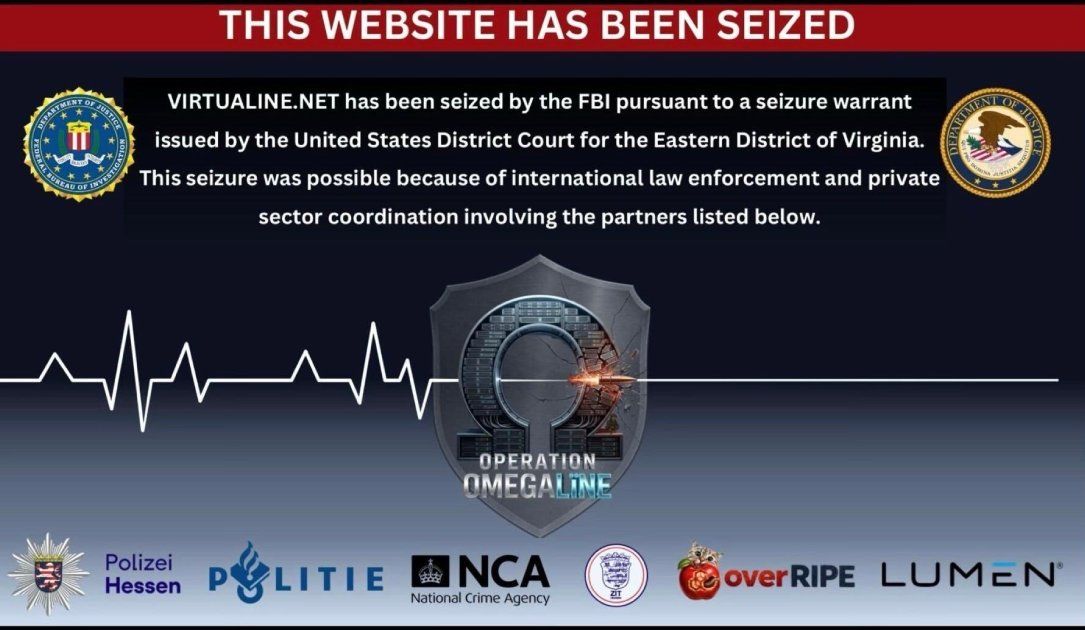
FBI seizes Virtualine domain tied to alleged cybercrime and other criminal activities
U.S. authorities seize the domain of Virtualine, a so-called “bulletproof” hosting service used to support criminal activity. Multiple outlets report the FBI is behind the action,...

Drupal warns of actively exploited critical Commerce Core authorization bypass
Drupal warns that a highly critical security flaw in its Commerce Core module is being exploited in the wild against online stores. The issue involves an authorization or access by...

Hackers exploit Cisco SD-WAN vulnerability to deploy KeyDrift malware targeting encryption keys
Hackers exploit a vulnerability in Cisco Catalyst SD-WAN Controllers to deploy a custom malware framework known as KeyDrift, security reporting says. The activity uses CVE-2026-201...
Sony ISP So-net breach exposes about 2.5–2.6 million customer records
Sony Network Communications, which runs Japan’s So-net and Plala, confirms an information leak after unauthorized access to its member database. Multiple outlets report that custom...

Volt Typhoon uses rotating “Silent Train” relay network to target enterprise and infrastructure
Volt Typhoon, described by multiple researchers as a China-linked, state-sponsored cyberespionage group, is using a covert relay framework called “Silent Train” to conceal intrusio...
UNM Health restores systems after ransomware attack disrupts hospital care
The University of New Mexico Health Sciences Center says it restores systems after a cyberattack that disrupts hospital operations, including patient-care services. Coverage across...

Hackers probe patched Oracle E-Business Suite vulnerability days after CVE-2026-101767 fix
Hackers begin probing systems for CVE-2026-101767, a recently patched vulnerability in Oracle E-Business Suite (EBS), with multiple outlets reporting early scanning and exploratory...

Cisco patches actively exploited ASA and FTD SSL VPN zero-day flaw
Cisco releases security updates to patch a denial-of-service zero-day vulnerability affecting its Secure Firewall ASA and FTD software used for remote access SSL VPN. The flaw is b...
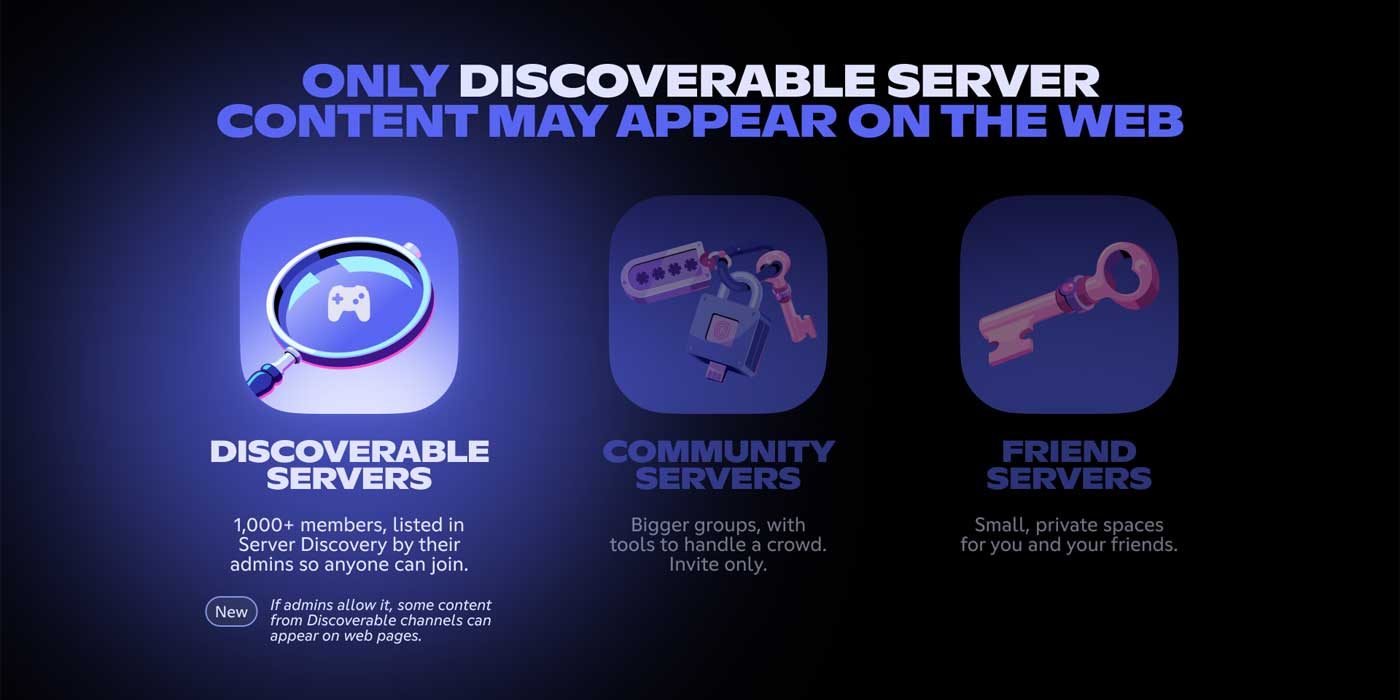
Discord to let search engines index messages from public Discoverable Servers
Discord says messages posted in its largest public “Discoverable Servers” will be indexed by Google and other search engines starting in mid-December. Users’ conversations may appe...
GMO Internet warns customers to disconnect PCs after ransomware threat tied to Onamae breach
Japan’s GMO Internet tells customers to shut down and disconnect their PCs after hackers threatened a ransomware attack connected to a breach of its Onamae Desktop Cloud service. M...
Ukrainian hacker Artem Stryzhak sentenced to 70 months for Nefilim ransomware role
A Ukrainian national, Artem Stryzhak, is sentenced to 70 months in US prison after pleading guilty in connection with ransomware activity involving Nefilim and the Hive ecosystem....

Tailscale patches SSH vulnerabilities that could allow root-level access via forwarding
Tailscale has released fixes for vulnerabilities in its built-in SSH server that could allow an attacker who already has access to a device in a tailnet to reach services and files...

CISA warns of active exploitation of critical Node2Shell Brotli vulnerability
The US Cybersecurity and Infrastructure Security Agency (CISA) warns that hackers are actively exploiting a critical Brotli compression flaw known as Node2Shell, with related names...
DreamHost forces email and FTP password resets after File Manager disruption
DreamHost is requiring forced password resets for email and FTP/SFTP users after an ongoing incident that started with connectivity problems in its File Manager interface on Octobe...
Brotli RCE flaw prompts emergency patches across Node.js, .NET, and Python ecosystems
Multiple outlets report that a critical vulnerability in Google’s open-source Brotli compression library is being actively patched across major software ecosystems. The flaw is des...

Apple backports fixes for exploited CoreGraphics vulnerability to older iPhones and iPads
Apple backports security fixes for a high-severity CoreGraphics flaw that has been exploited in real-world attacks to older iPhones and iPads. The vulnerability, identified as CVE-...
University of Copenhagen confirms breach exposing personal data of about 525,000 people
The University of Copenhagen (UCPH) says a cyber incident exposed personal data tied to roughly 525,000 people. Multiple outlets report that hackers accessed a test environment con...

Researchers disable abandoned Popcorn Time updater after it posed botnet risk
Researchers report that a background “updater” component in the abandoned Popcorn Time fork known as Time4Popcorn could be abused to execute code on infected computers. They descri...

Malicious AGENTS.md files in Downloads trick AI coding agents into installing malware
Several outlets report that a malicious instruction file named AGENTS.md placed in a user’s Downloads folder can trick AI coding agents into running harmful commands, including ins...