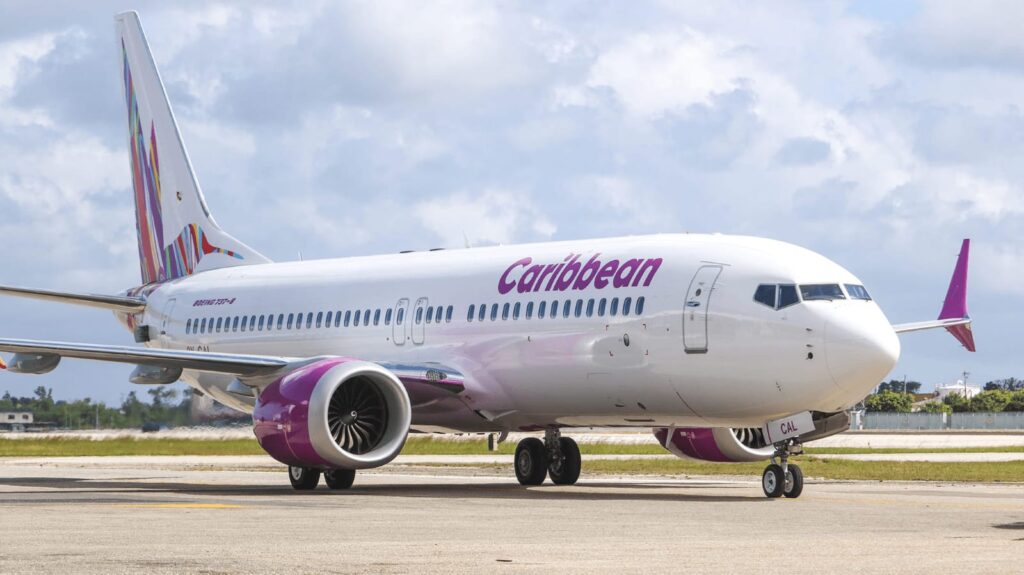
Caribbean Airlines says it has been informed by its reservations service provider, Amadeus IT Group, that an unauthorised party accessed some customers’ booking and reservation information following a cyberattack exploiting a vulnerability.
The reports describe the incident as reaching reservation-related data rather than payment details. Caribbean Airlines’ communications, as reflected in the outlets, indicate early findings that payment card information was not taken.
Across the coverage, outlets largely align on what was accessed (booking and reservation data) and on the role of Amadeus as the attacked third-party provider. Differences mainly appear in emphasis: one outlet leads with the broader “travel data exposed” framing, while others foreground the airline’s confirmation and the specific point that card details were unaffected.