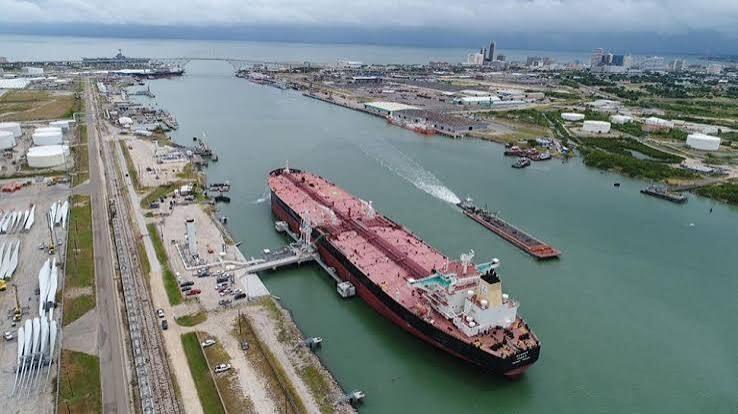
Hackers are launching “hundreds or even thousands” of attempted cyber intrusions targeting U.S. ports, with the Port of Corpus Christi in Texas reporting the highest volume. Port of Corpus Christi chief executive Kent Britton tells the Financial Times that the port is targeted on a daily basis as attackers focus on systems supporting crude exports and cargo operations.
The reporting is set against a broader pattern of cyber incidents affecting U.S. infrastructure and maritime activity. Other U.S. entities and incidents mentioned across coverage include investigations by the FBI, an alleged cyberattack attempt involving the Algonquin Dam, and an earlier cyberattack on the North Carolina State Ports Authority that led to manual gate processing at multiple ports. Reuters is also cited describing Coast Guard and FBI actions after suspected compromise of networks on foreign-flagged tankers in the Gulf of Mexico.
Outlets largely align on the scale of attempts described by the Port of Corpus Christi and the wider context of increased cyber pressure on infrastructure and trade routes. Differences are mainly in emphasis: some foreground the strategic risk to oil exports and port operations, while others frame the issue as part of a broader rise in AI-enabled attacks against critical systems.