
Infosecurity Magazine
What it covers
Latest stories it covered

UK warns AI-powered ransomware attacks on critical infrastructure likely by 2028
The UK’s National Cyber Security Centre (NCSC) warns that AI-powered ransomware attacks targeting critical national infrastructure are “highly likely” by 2028, according to its ann...

China-aligned hackers exploit Sogou Input Method via DNS hijacking to deliver malware
A security report says a China-aligned threat group uses a DNS hijacking technique to abuse the Sogou Input Method, turning branded online content into a delivery route for malicio...

3AM ransomware attack strikes UK school estate using suspected AI-assisted tactics
A ransomware attack at about 3 a.m. hits a UK school estate, with reports describing suspected AI-assisted activity alongside traditional intrusion steps. Infosecurity Magazine say...
Europol-backed police seize 100-plus servers in European investment fraud investigation
Police across Europe seize more than 100 servers and arrest seven people in connection with an alleged cross-border investment fraud scheme. The operation is linked to a reported o...
Binance says North Korean hackers used fake job interviews to steal about $6.3B
Cryptocurrency exchange Binance says a record $6.3 billion theft was enabled by a multi-stage hacking campaign that included a fake job interview and malware delivered to an employ...

Google warns LLMjacking attacks can rack up up to $1 million in cloud charges
Google says attackers are hijacking enterprise access to large language model (LLM) services, then using the accounts to generate large, fraudulent cloud bills. In some cases, vict...

BTCPay Server warns merchants as hackers drain hot wallets on outdated instances
Hackers steal cryptocurrency by draining “hot wallets” from outdated BTCPay Server installations, prompting the project to urge operators to take immediate action. Multiple outlets...
Bitter APT uses PapRAT in South and Southeast Asia cyber-espionage campaign
Security researchers report that the Bitter threat group deploys PapRAT as part of a cyber-espionage campaign targeting organizations in South and Southeast Asia. The reporting des...

Fake ChatGPT and Claude apps deliver Yoba malware and cryptocurrency miners
Fake ChatGPT and Claude “desktop apps” are being used to spread malware to people looking to try AI tools. Across multiple outlets, coverage says attackers create lookalike project...
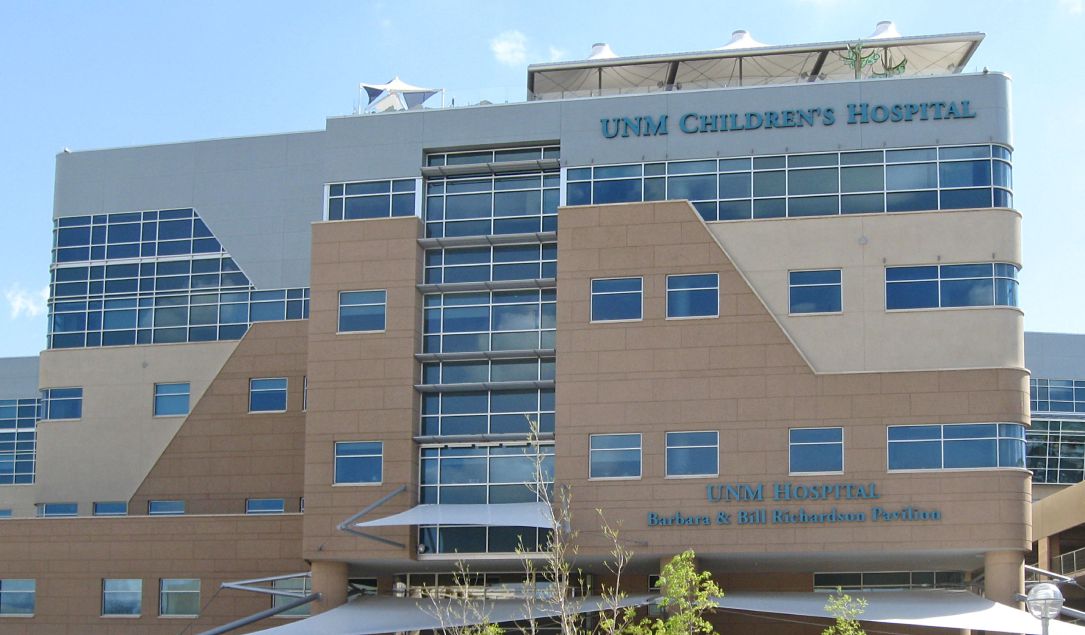
UNM Health restores systems after ransomware attack disrupts hospital care
The University of New Mexico Health Sciences Center says it restores systems after a cyberattack that disrupts hospital operations, including patient-care services. Coverage across...
GMO Internet warns customers to disconnect PCs after ransomware threat tied to Onamae breach
Japan’s GMO Internet tells customers to shut down and disconnect their PCs after hackers threatened a ransomware attack connected to a breach of its Onamae Desktop Cloud service. M...

Hackers Infect 953 Online Stores With Scanner-Evading JavaScript Loader
Hackers infect 953 online stores with a scanner-evading JavaScript loader, a campaign that has been active since July 2025. The activity involves adding a small piece of code to st...

CISA releases CISA 2030 strategy to strengthen critical infrastructure cyber defense
The Cybersecurity and Infrastructure Security Agency (CISA) has released “CISA 2030: Defend, Harden, Prevail,” a strategy aimed at improving the security and resilience of U.S. cri...
University of Copenhagen confirms breach exposing personal data of about 525,000 people
The University of Copenhagen (UCPH) says a cyber incident exposed personal data tied to roughly 525,000 people. Multiple outlets report that hackers accessed a test environment con...

Gheist campaign uses stolen GitHub tokens to exfiltrate secrets from private repos via Actions logs
A supply chain-style campaign called “Gheist” uses stolen GitHub access tokens to plant GitHub Actions workflows that print repository secrets into logs, which attackers then downl...
Blue Initiative launches free vulnerability database for maritime ship and port IT/OT systems
The Blue Initiative launches a free vulnerability database focused on information technology (IT) and operational technology (OT) vulnerabilities affecting ship and port systems. T...
PHP releases emergency fixes for critical unauthenticated RCE flaws dubbed PHP2Shell
PHP releases emergency patches for two critical vulnerabilities in PHP core that can allow unauthenticated remote code execution (RCE). The issues, dubbed “PHP2Shell,” are assigned...

Capcom confirms data breach affecting about 11.7 million CAPCOM ID accounts
Capcom confirms an unauthorised data breach involving its CAPCOM ID account service, with coverage across outlets putting the affected total at about 11.7 million users (often desc...
Microsoft links ConnectWise supply-chain attack to Chinese hackers using ARTEX AI tool
Microsoft says the ConnectWise Cloud Backup supply-chain compromise was carried out by a China-state-aligned hacker group known as Storm-0940 using ARTEX, an AI-enabled penetration...

Hackers hijack exposed AI models to run more autonomous cyberattacks
Hackers are using exposed, internet-accessible AI models as part of automated cyberattacks, according to Symantec research described by multiple outlets. The reported approach invo...