
SecurityWeek
What it covers
Latest stories it covered

Google expands Cloud VRP with a new $250,000 reward for root-in-cloud bugs
Google expands its Cloud Vulnerability Reward Program (VRP) by adding a new top-tier payout for certain high-impact “root-in-cloud” vulnerabilities. The additional reward is set at...
Polymarket to refund $3.9 million after hijacked DebugBear script compromise
Polymarket says it will refund about $3.9 million to traders after a security incident on October 29 involving malicious code distributed through a third-party script. The company’...
CISA adds two exploited Ivanti Connect Secure flaws to KEV catalog as Ivanti issues patches
CISA tells U.S. federal agencies to remediate two Ivanti Connect Secure vulnerabilities it adds to its Known Exploited Vulnerabilities (KEV) catalog. The flaws, CVE-2026-111357 and...

Anthropic Claude Code extension tampered in Cursor marketplace installs persistent SSH backdoor
A tampered version of Anthropic’s Claude Code VS Code-compatible extension appears in Cursor’s extension marketplace and attempts to install a persistent SSH backdoor on developer...
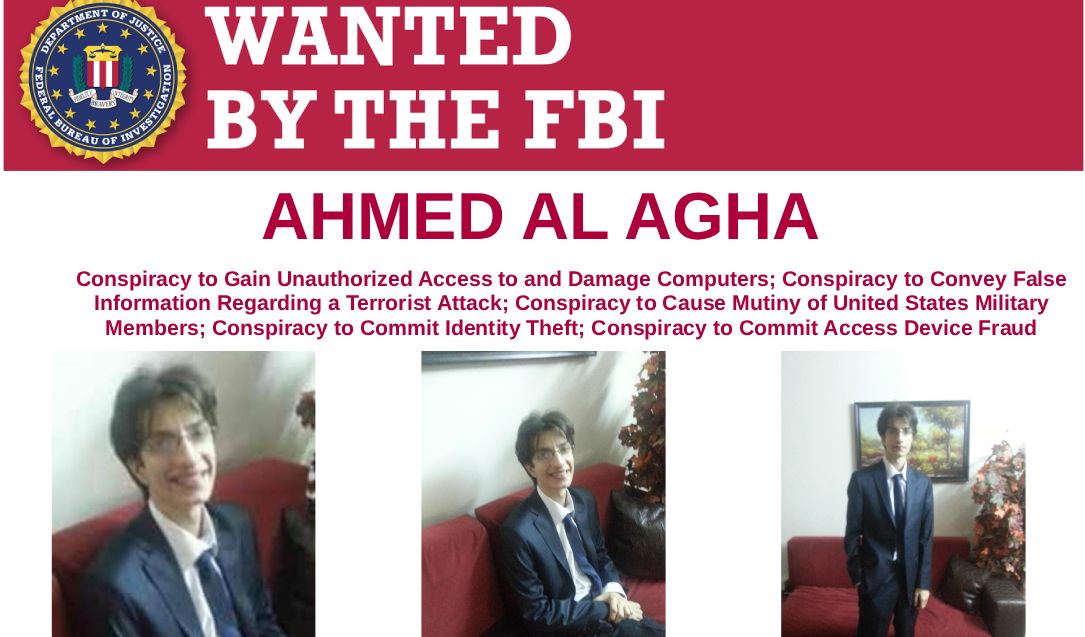
Syrian hacker Ahmad Umar Agha sentenced to 42 months in US for attacks and fake news posts
A U.S. federal court sentences Syrian hacker Ahmad Umar Agha, also known online as “Th3Pr0,” to 42 months in prison for a conspiracy involving pro-Assad cyberattacks and deceptive...

Anthropic files for a US IPO, highlighting rapid growth, major losses, and extensive risk disclosures
Anthropic, the company behind the Claude AI system, has filed paperwork to go public in the United States, with outlets focusing on what the filing reveals about growth, finances,...

Google unveils Gemini 4 Carbon, rolling it out first to vetted cyber defenders
Google has announced Gemini 4 Carbon, a new frontier AI model from DeepMind, presenting it as a “significant leap” in long-horizon coding and cybersecurity. Multiple outlets say th...
Hackers claim leaked data exposes about 41,000 DHS employees, including undercover personnel
Multiple outlets report that a hacking group has published or shared personal and work-related information tied to more than 40,000 U.S. Department of Homeland Security (DHS) emplo...

TeamViewer patches flaw that lets controlled hosts attack remote controller machines
TeamViewer has fixed a security vulnerability that can be abused during remote-support sessions. According to reporting, the host machine—the one being controlled—can exploit the f...
PHP2Shell RCE flaws exploited against Palo Alto Networks management interfaces and other targets
Multiple security outlets report that attackers are exploiting PHP2Shell—two newly patched critical PHP remote code execution (RCE) flaws, CVE-2026-109618 and CVE-2026-109619—to co...
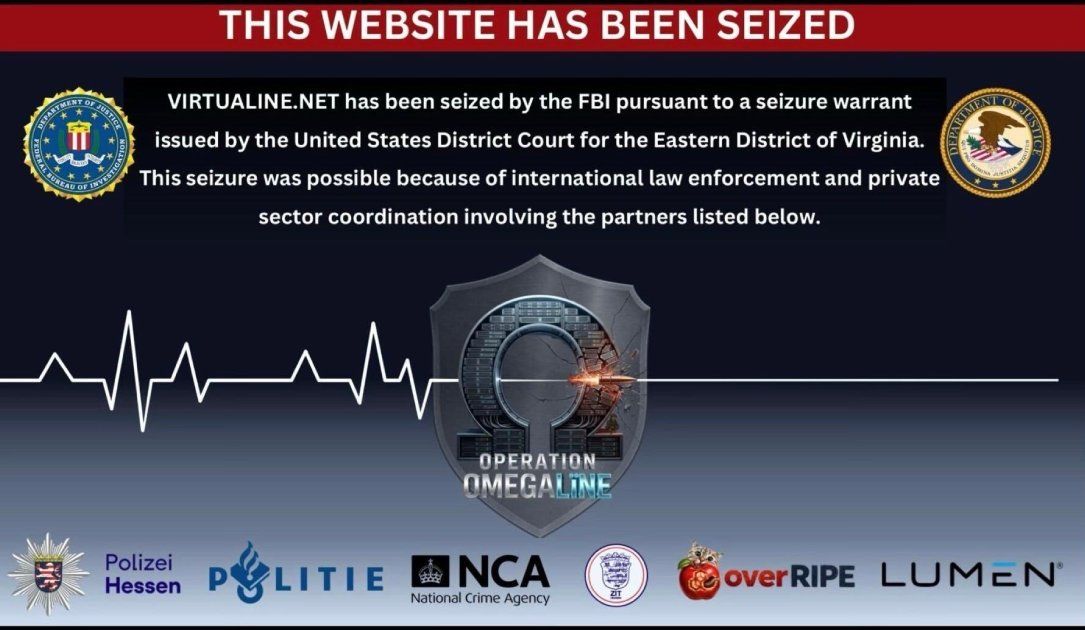
FBI seizes Virtualine domain tied to alleged cybercrime and other criminal activities
U.S. authorities seize the domain of Virtualine, a so-called “bulletproof” hosting service used to support criminal activity. Multiple outlets report the FBI is behind the action,...

Drupal warns of actively exploited critical Commerce Core authorization bypass
Drupal warns that a highly critical security flaw in its Commerce Core module is being exploited in the wild against online stores. The issue involves an authorization or access by...

CVE-2026-97229 GitLab flaw tied to attempted exploitation on Alpine Linux
A GitLab vulnerability tracked as CVE-2026-97229 is described as being exploited or attempted against Alpine Linux systems, with impacts involving arbitrary code execution on a Git...

China-nexus attackers exploited VMware ESX logging flaw to evade detection, researchers and agencies say
Attackers linked to China use a VMware ESX/ESXi logging flaw to reduce audit-trail visibility, according to cybersecurity researchers and reporting by multiple outlets. The issue i...
BAE Systems says no data was extracted after cyber intrusion affecting U.S. bankruptcy courts
BAE Systems says a cyber intrusion into its systems for federal bankruptcy courts did not involve data extraction. In statements to Recorded Future News, a spokesperson said “no da...
Sony ISP So-net breach exposes about 2.5–2.6 million customer records
Sony Network Communications, which runs Japan’s So-net and Plala, confirms an information leak after unauthorized access to its member database. Multiple outlets report that custom...

Volt Typhoon uses rotating “Silent Train” relay network to target enterprise and infrastructure
Volt Typhoon, described by multiple researchers as a China-linked, state-sponsored cyberespionage group, is using a covert relay framework called “Silent Train” to conceal intrusio...
UNM Health restores systems after ransomware attack disrupts hospital care
The University of New Mexico Health Sciences Center says it restores systems after a cyberattack that disrupts hospital operations, including patient-care services. Coverage across...

Hackers probe patched Oracle E-Business Suite vulnerability days after CVE-2026-101767 fix
Hackers begin probing systems for CVE-2026-101767, a recently patched vulnerability in Oracle E-Business Suite (EBS), with multiple outlets reporting early scanning and exploratory...

Cisco patches actively exploited ASA and FTD SSL VPN zero-day flaw
Cisco releases security updates to patch a denial-of-service zero-day vulnerability affecting its Secure Firewall ASA and FTD software used for remote access SSL VPN. The flaw is b...