
The Hacker News
What it covers
Latest stories it covered

Cisco patches actively exploited ASA and FTD SSL VPN zero-day flaw
Cisco releases security updates to patch a denial-of-service zero-day vulnerability affecting its Secure Firewall ASA and FTD software used for remote access SSL VPN. The flaw is b...

GitHub previews npm package firewall to block malicious packages during installation
GitHub is introducing an npm package firewall in public preview that aims to stop suspicious packages before they install. The feature inspects package metadata requests and the pa...

Critical EDK II UEFI firmware flaw could allow early code execution on network-boot servers
A critical vulnerability in EDK II UEFI firmware could let attackers execute malicious code early in the boot process, before an operating system loads. Multiple outlets describe t...

Logic flaws let a Pwn2Own winner achieve code execution outside Edge’s sandbox
A security researcher says a Pwn2Own-winning chain of logic bugs in Microsoft Edge can lead to code execution on a Windows computer outside the browser’s sandbox. Orange Tsai of DE...
GMO Internet warns customers to disconnect PCs after ransomware threat tied to Onamae breach
Japan’s GMO Internet tells customers to shut down and disconnect their PCs after hackers threatened a ransomware attack connected to a breach of its Onamae Desktop Cloud service. M...

Security advisory finds TLS flaws in GoAhead web server affecting some devices
Researchers say they have found multiple TLS weaknesses in the GoAhead embedded web server, which is used in large numbers of devices. The reported issues involve how the server ha...

Tailscale patches SSH vulnerabilities that could allow root-level access via forwarding
Tailscale has released fixes for vulnerabilities in its built-in SSH server that could allow an attacker who already has access to a device in a tailnet to reach services and files...

Hackers impersonate IT support in Microsoft Teams external chats to take remote control
Attackers are using Microsoft Teams’ external chat feature to impersonate IT support and, in hundreds of cases, move from chat to hands-on access of victims’ devices. Security firm...

Researchers say CyberStrikeAI used 44 AI agents in attacks targeting Japan
Cybersecurity researchers report that a threat actor known as “CyberStrikeAI” used a system involving 44 AI agents to automate parts of hacking operations against targets in Japan....

Microsoft Authenticator Android flaw let malicious apps steal work account session tokens
Microsoft has fixed a vulnerability in its Authenticator app for Android that researchers say could allow a malicious application to obtain authentication tokens for a user’s work...
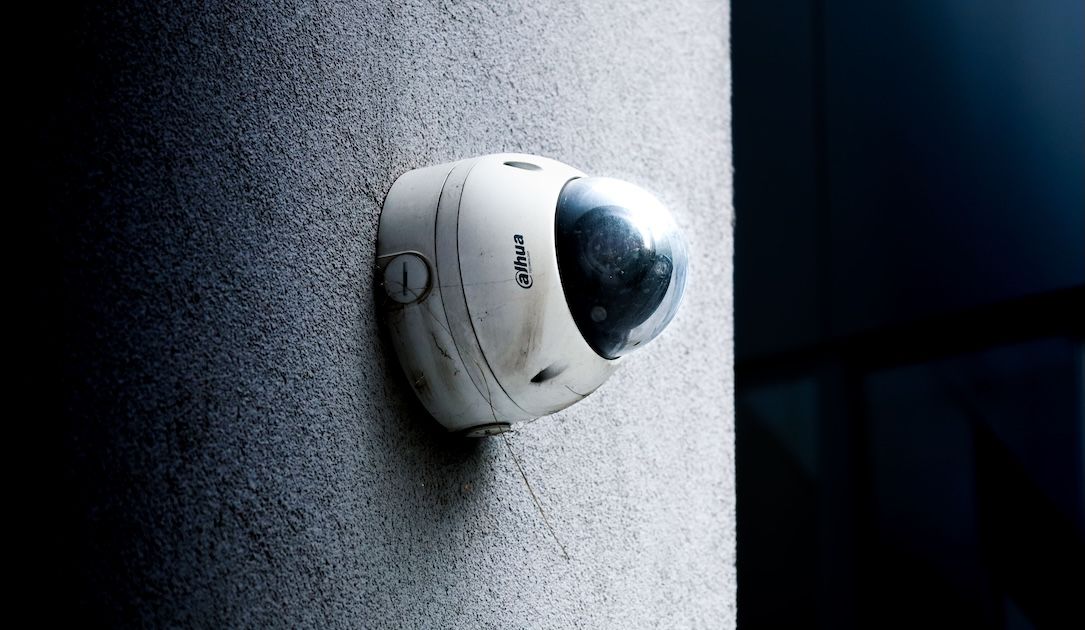
Ukraine warning: Dahua IP cameras hijacked via Easy4IP P2P and authentication weaknesses
Ukrainian cybersecurity authorities warn that attackers are hijacking Dahua IP cameras, NVRs and DVRs accessed through Easy4IP’s P2P cloud relay. CERT-UA says intruders compromise...

Keystone pulls some hardware wallets after stolen key enables counterfeit verification
Keystone, the maker of cryptocurrency hardware wallets, says hackers stole a device verification key that helps its wallets prove they are genuine. With that key, attackers could p...

Apple backports fixes for exploited CoreGraphics vulnerability to older iPhones and iPads
Apple backports security fixes for a high-severity CoreGraphics flaw that has been exploited in real-world attacks to older iPhones and iPads. The vulnerability, identified as CVE-...

Hackers Infect 953 Online Stores With Scanner-Evading JavaScript Loader
Hackers infect 953 online stores with a scanner-evading JavaScript loader, a campaign that has been active since July 2025. The activity involves adding a small piece of code to st...
Google privacy policy adds exception allowing Gmail and Photos data to personalise targeted ads
Google updates its privacy policy to clarify that Gmail, Drive and Google Photos data may be used to personalise targeted ads when users opt in to connected “Personal Intelligence”...

Gheist campaign uses stolen GitHub tokens to exfiltrate secrets from private repos via Actions logs
A supply chain-style campaign called “Gheist” uses stolen GitHub access tokens to plant GitHub Actions workflows that print repository secrets into logs, which attackers then downl...

Researchers disable abandoned Popcorn Time updater after it posed botnet risk
Researchers report that a background “updater” component in the abandoned Popcorn Time fork known as Time4Popcorn could be abused to execute code on infected computers. They descri...

Malicious AGENTS.md files in Downloads trick AI coding agents into installing malware
Several outlets report that a malicious instruction file named AGENTS.md placed in a user’s Downloads folder can trick AI coding agents into running harmful commands, including ins...
OpenAI resumes frontier AI training with stricter security and no live internet access
OpenAI is restarting training of its most advanced (“frontier”) AI systems after a security overhaul, while keeping the models from accessing the live web. Multiple outlets report...

Arista patches actively exploited VeloCloud Orchestrator SQL injection after CISA KEV listing
Arista issues security updates to address a SQL injection vulnerability in its VeloCloud Orchestrator (VCO) that Arista says is actively exploited. The company assigned CVE-2026-11...