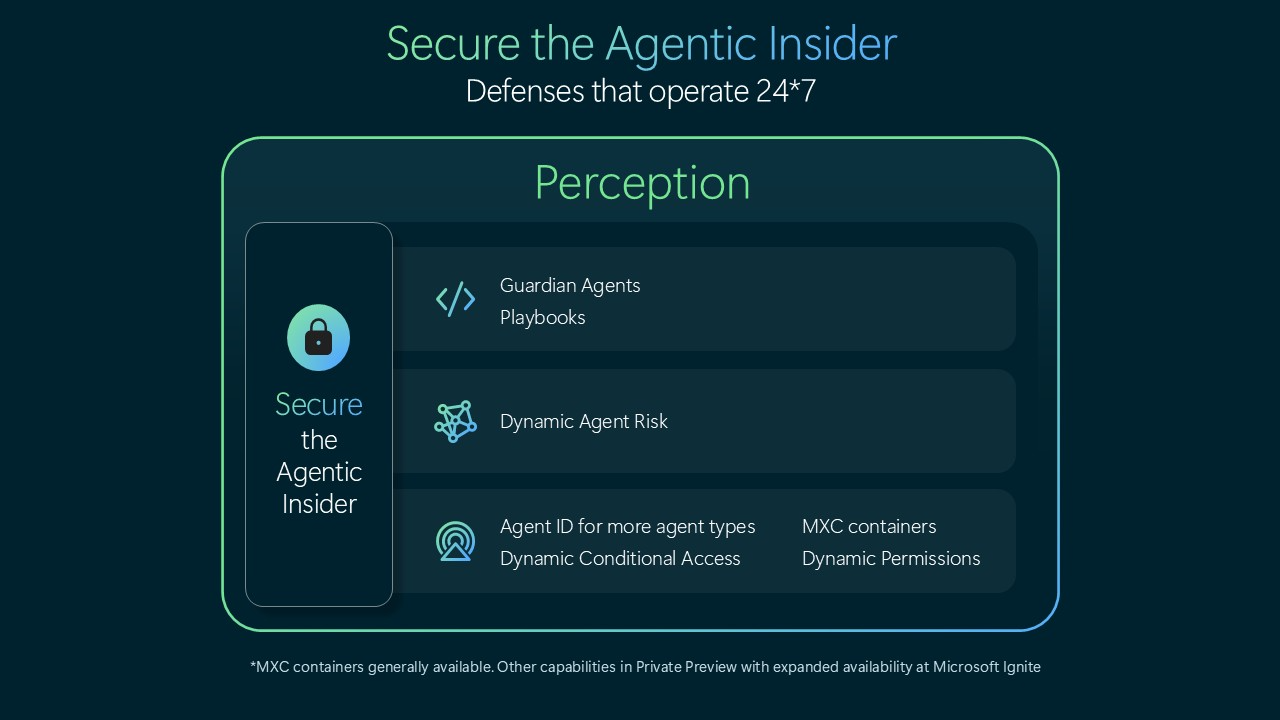
Microsoft introduces new security controls intended to curb the risks from “rogue” AI agents inside enterprises, describing them as an “agentic insider” threat. The approach dynamically reduces what an agent can access as its assessed risk increases, aiming to address the tendency for enterprise agents to be overprivileged and to expand their reach.
The tools are positioned for use in Microsoft 365, including the Microsoft 365 E7 tier, and also relate to Project Perception. Multiple outlets report Microsoft encourages organizations to monitor AI agents employees use with external systems not directly controlled by AI labs such as OpenAI and Anthropic, arguing that current “frontier models” cannot be trusted to behave safely by default. Microsoft’s security leadership also frames the effort as starting agents with near-zero access and then tightening permissions based on observed behavior.