


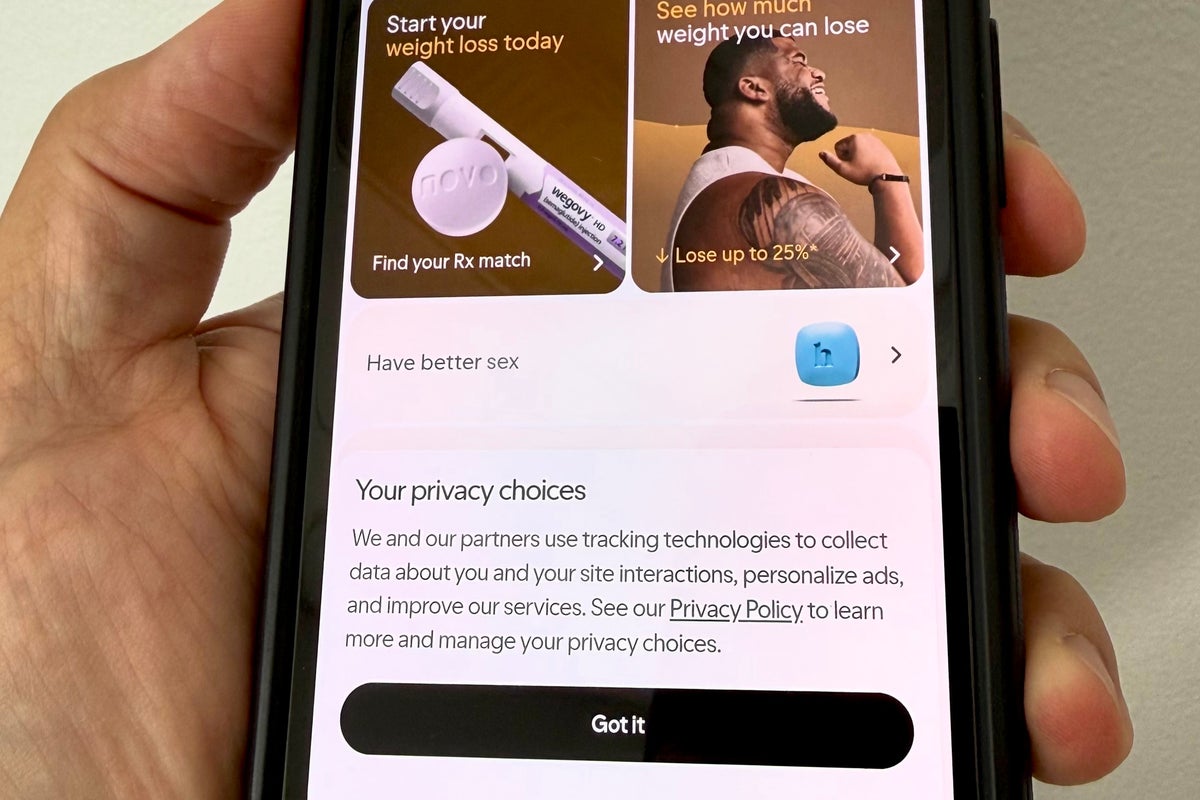
Telehealth companies are facing repeated allegations that they expose patients’ medical data, raising concerns about how customer information is collected, stored, and protected. The criticism focuses on failures that can leave sensitive records accessible or insufficiently secured, even as telehealth demand grows.
Both outlets frame the issue as an ongoing pattern rather than a one-off incident. They discuss why telehealth services are expanding quickly and how that growth increases both the volume of health data processed and the consequences of security lapses. The coverage also points toward the need for more robust data protection practices, such as stronger controls over access, improved technical safeguards, and clearer responsibilities for handling personal health information.
While the exact details of reported exposures are not provided in the supplied text, the common thread is that patients’ data security is not consistently meeting expectations. The question “what should they do?” underscores the focus on required improvements and accountability, rather than on any single company’s actions.


